Pseudonymization
Identifiers are removed before an application receives anything. Your staff see patient names in the platform's own screens, resolved outside the application's frame, and that reveal is recorded.
WorkingTrust
This page is written for the people whose job is to say no. Where a control is enforced, it says what enforces it. Where it is designed and not yet enforced, it says that instead.

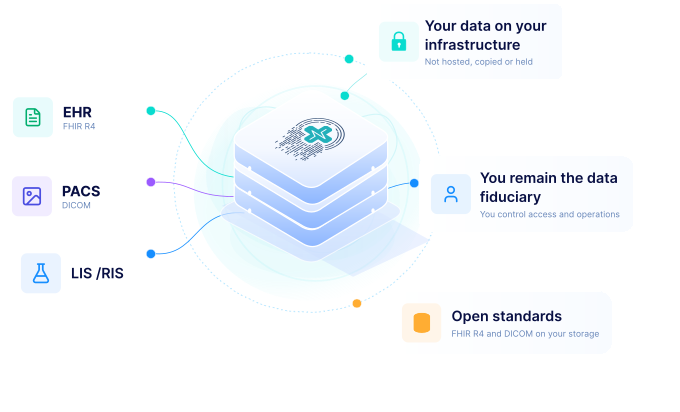
The platform runs on your infrastructure. Nexus does not host, copy or hold your patient data or backups.
You remain the data fiduciary. Nexus provides the controls, the evidence and the operations.
Your clinical data is held in open standards — FHIR R4 and DICOM — on your own storage, so leaving does not mean extracting.
Termination and data-handling terms to be published
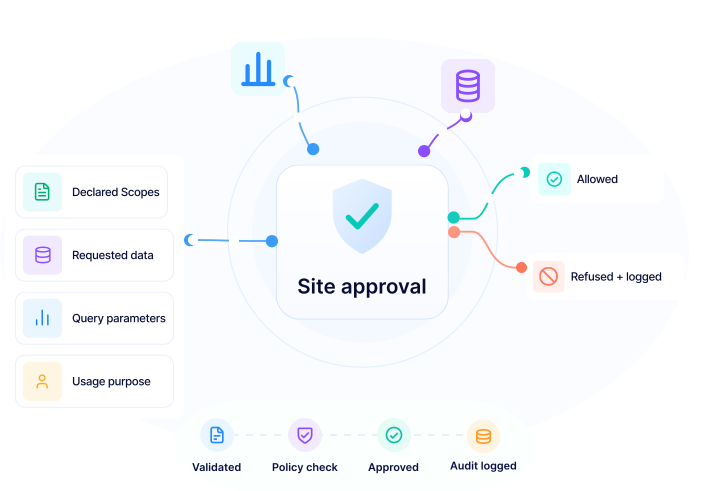
An application declares the resources it needs in its manifest. Your administrator approves them. Every request is checked against that approval, and a request outside it is refused and recorded.
Declared scopes, approved per site
WorkingPseudonymization before an application receives data
WorkingAggregate-only scopes, enforced in the query engine
WorkingRefusals written to the audit ledger
WorkingRepeated violations suspend the application
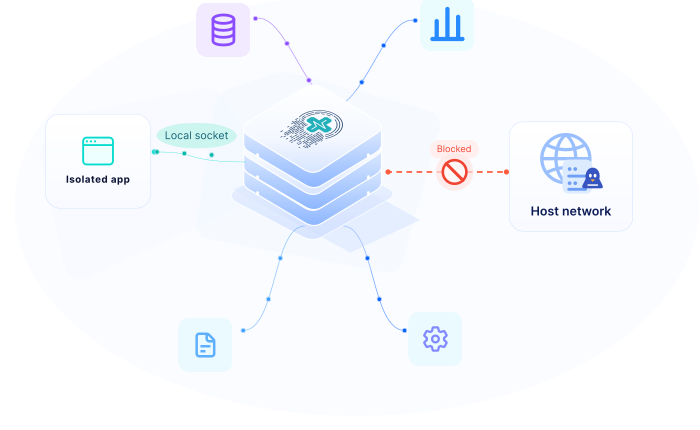
WorkingEach application process is started inside its own empty network namespace on the Linux host: no network interface, no route, nothing to send to. Its only channel is a local socket to the platform. The platform verifies this against the operating system every time an application starts, and refuses to start one on a host where it cannot.
Working on Linux, which is what the platform runs on
Our test suite includes an application that genuinely carries an HTTP client and tries to reach a listener on the host. On a Linux host it fails. We will run that test with your security team, on your hardware.
Identifiers are removed before an application receives anything. Your staff see patient names in the platform's own screens, resolved outside the application's frame, and that reveal is recorded.
WorkingWhere an application is approved for counts rather than records, a plain record search is refused, and grouped results have small cells and their complements removed inside the query engine before they leave it.
WorkingThere is no query budget, and the differencing defence has not had an external review.
An application proposes. A person approves in the platform's own screen. Only then does the platform re-identify and write to the source system, and every step is recorded.
WorkingA hash-chained core with a validated clinical event catalogue above it. Applications never write it. The chain and its signed checkpoints can be verified by your own team.
WorkingNo application updates itself; every new version needs your approval. A host readiness check reports which controls hold on your hardware and which fall back.
WorkingSend security questions, architecture review requests and vulnerability reports to a monitored address.
WorkingCertifications
Nexus makes no certification or regulatory claim it does not hold. This table will say exactly this until the day it changes.
ISO 27001
SOC 2
Independent penetration test
Medical device clearance for Nexus-built applications
Data processing agreement
Sub-processors
Research features are for research use and not for clinical care. Nexus does not claim unrestricted access to institutional data, and the default posture is the restrictive one.
See how Nexus can help your organization unlock the value of clinical data with AI — securely and at scale.
For hospitals · research institutions · healthcare AI companies